For continuous-process plants in Saudi Arabia, DCS upgrade services Saudi Arabia teams can trust should start with a structured review of installed hardware, software versions, network architecture, historian and HMI dependencies, backup validity, and shutdown constraints before anyone touches the live system. That approach matches current OT guidance, which stresses risk-based decisions around performance, reliability, and safety, and it also matches vendor lifecycle guidance that treats upgrade work as an engineering and serviceability exercise rather than a simple software refresh.
That matters because most upgrade failures do not begin with the controller itself. They usually begin with unclear as-built documentation, unsupported versions, fragile interfaces, incomplete backups, untested cutover logic, or field loops that were never fully validated after earlier modifications. A strong upgrade scope should therefore cover architecture review, integration checks, commissioning evidence, cybersecurity process, and post-upgrade support, not only the new revision number.
If the project will touch your main control layer, start from Distributed Control System (DCS) and review connected Monitoring System (SCADA, HMI) functions at the same time, because many upgrade problems appear at the interface between them, not inside one node alone.
What to check before planning a DCS upgrade
The first check is whether the plant actually knows its current installed base. A proper review should identify controller generations, server roles, engineering stations, operating systems, network paths, historians, alarm servers, HMI nodes, third-party interfaces, and any PLC or package-unit dependencies. Current OT guidance emphasizes understanding system architecture, interconnections, and operational dependencies before making changes in production environments.
The second check is serviceability. Official assessment and modernization material for process-control systems focuses on recovering or improving serviceability, availability, and lifecycle support, which is often the real reason plants start considering upgrades in the first place. If spare parts, software support, backup tools, or qualified support routes are weak, the plant is already carrying operational risk even if production is still stable.
The third check is documentation quality. Before any change window, the plant should be able to confirm at least these items:
- current architecture and network drawings
- validated backups and restore method
- I/O and tag mapping
- historian and alarm dependencies
- cause-and-effect or sequence logic references
- tested rollback assumptions
- shutdown window and startup prerequisites.
A practical supporting reference for field readiness is pre-commissioning checklist for instrumentation, because many “DCS upgrade” problems turn out to be unresolved instrument, loop, or field-interface issues when startup begins.
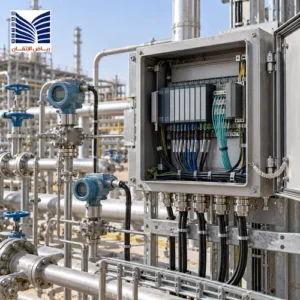
Common issues during DCS upgrade services Saudi Arabia
1) Unsupported or weak backups
One of the most dangerous situations is assuming a backup is valid without proving it can be restored. In live plants, this is often the difference between a manageable upgrade and a major outage. OT security and lifecycle guidance both treat backup integrity and controlled maintenance practice as core requirements, not optional extras.
If the plant cannot prove what is actually running, the safest next step is not an upgrade weekend. It is an engineering assessment.
2) HMI, historian, and alarm mismatches
A DCS can look healthy from the controller side while the operator layer is already failing. Official migration and modernization material repeatedly stresses mapping, software-component compatibility, and integrated software upgrade planning because historian links, alarm servers, graphics, and reporting tools are common weak points during system transitions.
This is why upgrade planning should include DCS system and SCADA systems dependencies, not just controller firmware.
3) Incomplete field validation
A surprising number of brownfield upgrades fail late because the site assumed loop readiness. Commissioning guidance from major process-control vendors highlights loop checks, off-line configuration validation, and field-device startup checks as major tools for reducing startup delay and catching issues before the plant goes live again.
That means an upgrade project should not rely only on software FAT. It also needs field-side validation, especially where earlier site changes were poorly documented.
4) Cybersecurity and access-control gaps
A DCS upgrade is also an OT change, so cybersecurity exposure can increase if remote access, user roles, patch governance, or network boundaries are not reviewed. NIST’s OT guide specifically addresses threats, vulnerabilities, and recommended countermeasures for DCS and other OT environments, while IEC 62443 service-provider requirements focus on secure processes during integration and maintenance.
For plants with remote visibility or plant-wide monitoring, it is smart to review SCADA security best practices alongside the upgrade plan.
5) Poor cutover and rollback logic
Many upgrade plans describe the target system but not the transition path. Official modernization guidance emphasizes reducing risk and avoiding downtime through structured migration planning, while migration material repeatedly treats downtime reduction as a function of preparation and staged execution, not optimism.
If the upgrade plan does not define who makes the go/no-go decision, what conditions trigger rollback, and how to restore the previous safe state, the plan is incomplete.
Diagnostic checkpoints before you approve site work
Before signing off a DCS upgrade window, a plant team should verify these checkpoints:
Architecture checkpoint
Confirm all nodes, networks, interfaces, and external packages that the DCS depends on. OT guidance explicitly recommends understanding connected assets and operational dependencies before modifying live environments.
Version checkpoint
Confirm the exact upgrade path, supported combinations, and any integrated software components that must move together. Modernization guidance from official vendor pages makes clear that reliable upgrades depend on supported paths and integrated software treatment.
Commissioning checkpoint
Confirm FAT, SAT, loop checks, interlock checks, and startup responsibilities. Commissioning support material shows that loop and field validation directly reduce delay and startup burden.
Security checkpoint
Confirm remote access rules, account handling, backup discipline, and maintenance controls. OT and IEC 62443 guidance both treat these as operational requirements, not side tasks.
Support checkpoint
Confirm who supports the plant after startup, how changes are documented, and how serviceability is maintained. Lifecycle service material explicitly ties upgrades to ongoing support, training, maintenance, and documentation control.
Risk indicators that mean you should stop patching and escalate
A plant should stop treating the issue as routine and bring in a specialist team when one or more of these signs appear:
- nobody can verify that the backup matches the running system
- HMI, historian, or alarm behavior changed after minor edits
- controller or server versions are unsupported or partially supported
- remote access or cybersecurity controls are informal or unclear
- previous site modifications were not fully documented
- the upgrade scope touches critical units with limited shutdown tolerance
- there is no tested rollback path.
Those are not ordinary maintenance nuisances. They are system-risk indicators.
When to bring in a specialist team
A specialist team should be brought in when the upgrade affects multiple layers at once: controller software, HMI, historian, alarm handling, network architecture, third-party integrations, or startup sequence. It also makes sense when the site needs more than upgrade labor and instead needs assessment, migration planning, commissioning support, and lifecycle recovery. Official modernization material repeatedly frames these services as structured programs to reduce downtime and recover long-term supportability.
This is also where the difference between a generic DCS supplier Saudi Arabia option and a real DCS system integrator Saudi Arabia option becomes visible. A stronger team will usually connect the upgrade to industrial automation projects, electrical engineering services in Saudi Arabia, and the wider plant interface strategy instead of handling the DCS as an isolated product replacement.
Practical decision path for process plants
A service-first decision path usually works best:
- Audit the installed base and support status.
- Validate backups and documentation.
- Review HMI, historian, alarm, and interface dependencies.
- Confirm commissioning scope and field readiness.
- Define cutover and rollback logic.
- Escalate to specialist support if any of those areas are uncertain.
That sequence is usually faster and safer than pushing straight into implementation.
FAQ
What should be checked first in DCS upgrade services Saudi Arabia?
Start with the installed base, architecture, support status, backup validity, and dependent systems such as HMI, historians, and third-party interfaces. OT guidance and official modernization material both support that approach.
Why do DCS upgrades fail even when the core controller is fine?
Because many failures appear in interfaces, unsupported software combinations, undocumented changes, field loops, or operator-layer components rather than in the controller itself.
When does a plant need a specialist team instead of routine support?
When backups are uncertain, interfaces are fragile, the shutdown window is tight, or the change affects critical operating units with limited tolerance for failed cutover.
Should cybersecurity be part of a DCS upgrade services Saudi Arabia scope?
Yes. Current OT guidance and IEC 62443 service-provider requirements both treat cybersecurity process as part of responsible integration and maintenance.
If your plant needs structured DCS upgrade services Saudi Arabia teams can execute with lower risk, start with Distributed Control System (DCS) and review connected Monitoring System (SCADA, HMI) functions before committing to a shutdown window.